I updated the user-agent string indicator page to include Wireshark display filters using regex to find specific user-agents. I am by no means a regex pro, so if anyone finds any discrepancies or can figure out a cleaner way to search with regex, then please let me know.
A few things I noticed when using regex in Wireshark display filters. I was not able to figure out how to escape an open and close parenthesis (if I did escape those characters normally, it would not find the user-agent), so I had to do a logical AND plus another display filter in order to locate the right value (please see the Dyre user-agent string). Also, I had to be more explicit with the query with a shorted user-agent string value; meaning I had to add a Start of Line and End of Line character to the query.
I hope you all find this information useful, feel free to ask questions or leave comments. Thank you.
Monday, June 22, 2015

Tuesday, June 9, 2015
New User-agent Indicators Page
I made a post a few months back about malicious user-agent string values. It appears to be a pretty popular post, so I decided to create a page dedicated to malicious user-agent strings.
I added several more strings to the list as well as updating some regex. Speaking of which, I still need to add more regex values to that page and I will also add some Wireshark display filters that you can use to find user-agent strings in PCAP files.
I also added a new list on the right side of the page dedicated to just indicators. You can find the new page here. Enjoy!
I added several more strings to the list as well as updating some regex. Speaking of which, I still need to add more regex values to that page and I will also add some Wireshark display filters that you can use to find user-agent strings in PCAP files.
I also added a new list on the right side of the page dedicated to just indicators. You can find the new page here. Enjoy!
Monday, June 8, 2015
Indicators - Dridex
I have been seeing a large amount of emails containing malicious Microsoft Word macro-enabled documents attached. These documents, once the macro has been allowed to run by the user, will download and run an executable file to infect the machine. Below are several indicators that I have seen so far, and I have even created a Wireshark/regex filter that will help you find these files in a PCAP file.
Threat Name: Dridex
File Download Locations:
These files may no longer be active, but please use caution when downloading as they are malicious.
7sumur.com/73/20.exe
baypipo.com/55/55.exe
cellsitemanagement.com/73/20.exe
chiokings.com/88/15.exe
crestliquors.com/73/20.exe
croningroup.com/73/20.exe
dalmatian-bizhub.com/55/55.exe
deborah-abesser.com/88/15.exe
elkettasandassociates.com/25/10.exe
empreinte.com.ar/42/91.exe
footingclub.com/85/20.exe
hoinghihoithao.com/88/15.exe
jenisgroup.com/88/15.exe
joyofcamping.com/88/15.exe
kang-ning.com/353/654.exe
kapagrup.com/94/053.exe
m-bikes.gr.193-92-97-57.linuxzone26.grserver.gr/42/91.exe
mercury.powerweave.com/85/20.exe
mindfullivingprograms.com/73/20.exe
njgems.com/55/55.exe
orenkaholidays.com/5/0.exe
revistacannicas.com.ar/42/91.exe
seedsindaphne.org/85/20.exe
segurosdenotebooks.com.br/25/10.exe
thepattersonco.com/85/20.exe
tpsci.com/88/15.exe
tvteachervideos.com/42/91.exe
yubido.web.fc2.com/5/0.exe
zolghadri-co.com/25/10.exe
File Names:
The file names are numerical and 1 through 3 digits long.
0.exe
053.exe
10.exe
15.exe
20.exe
55.exe
654.exe
91.exe
Threat Name: Dridex
File Download Locations:
These files may no longer be active, but please use caution when downloading as they are malicious.
7sumur.com/73/20.exe
baypipo.com/55/55.exe
cellsitemanagement.com/73/20.exe
chiokings.com/88/15.exe
crestliquors.com/73/20.exe
croningroup.com/73/20.exe
dalmatian-bizhub.com/55/55.exe
deborah-abesser.com/88/15.exe
elkettasandassociates.com/25/10.exe
empreinte.com.ar/42/91.exe
footingclub.com/85/20.exe
hoinghihoithao.com/88/15.exe
jenisgroup.com/88/15.exe
joyofcamping.com/88/15.exe
kang-ning.com/353/654.exe
kapagrup.com/94/053.exe
m-bikes.gr.193-92-97-57.linuxzone26.grserver.gr/42/91.exe
mercury.powerweave.com/85/20.exe
mindfullivingprograms.com/73/20.exe
njgems.com/55/55.exe
orenkaholidays.com/5/0.exe
revistacannicas.com.ar/42/91.exe
seedsindaphne.org/85/20.exe
segurosdenotebooks.com.br/25/10.exe
thepattersonco.com/85/20.exe
tpsci.com/88/15.exe
tvteachervideos.com/42/91.exe
yubido.web.fc2.com/5/0.exe
zolghadri-co.com/25/10.exe
File Names:
The file names are numerical and 1 through 3 digits long.
0.exe
053.exe
10.exe
15.exe
20.exe
55.exe
654.exe
91.exe
IP Connections:
The malware will attempt to make CONNECT requests to the below IP addresses and ports.
144.76.238.214:4443
185.12.94.48:7443
185.12.95.191:4443
188.120.249.231:8443
70.32.74.108:7443
78.24.218.186:8443
78.46.60.131:4443
94.242.58.146:4443
Regex Query:
The following regex query should find the HTTP URI and file name of the executable file. Since the directory and file names are pretty consistent in the fact that they have been numerical values so far, it should be pretty easy to locate in your logs.
- \/[1-9]{1,3}\/[0-9]{1,3}\.exe
The following Wireshark display filter (using regex) should also work:
- http.request.uri matches "\/[1-9]{1,3}\/[0-9]{1,3}\.exe"
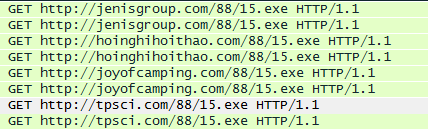
You should see similar information below in the Info column in Wireshark when you run the above query:
I am sure that I will be adding more indicators for this malware soon as it has been pretty prevalent over the past few weeks. Thanks for reading.
Wednesday, May 20, 2015
Bad Practice
I was surprised when I saw this one in some logs today. The smart phone application Parlor, exposes your username and password in the HTTP URI through their API, plain as day. These are what we like to call "easy wins" as they require no effort to find in standard event logs, and require no digging through the frames of PCAP files. Here is a screencap of the HTTP field:

Be careful when signing up for some of these applications on your smart phone, you never know what is exposed.

Be careful when signing up for some of these applications on your smart phone, you never know what is exposed.
Indicators - Geodo Malware Part 3
Since the last two updates I have collected a few more indicators, and I have decided to make an indicator page. I didn't want to create a tracking page, as there is a much better resource, rather I wanted to create a list of indicators that I have found. Below are a few new additions that I will be adding to the new Geodo indicator list; there are no new C2 servers or use-agent strings.
Link to the Geodo indicator page.
Threat Name: Geodo
File Download Locations:
These are live malware files, download with caution.
hXXp://obchod.vianatura.cz:80/YRgXCNup2zn8/9049.exe
hXXp://f3x.pl:80/modules/mod_aratipas/ex_mss3.exe
hXXp://zonaliberabraila.ro/ud3yRXLgSw2
hXXp://marjav.cl/g3aTdqlJI8
hXXp://intellinum.com/7UPYmxe150K
hXXp://blog.northpointindia.com/gKBwOvxeq
Further Reading:
rebus snippets
Link to the Geodo indicator page.
Threat Name: Geodo
File Download Locations:
These are live malware files, download with caution.
hXXp://obchod.vianatura.cz:80/YRgXCNup2zn8/9049.exe
hXXp://f3x.pl:80/modules/mod_aratipas/ex_mss3.exe
hXXp://zonaliberabraila.ro/ud3yRXLgSw2
hXXp://marjav.cl/g3aTdqlJI8
hXXp://intellinum.com/7UPYmxe150K
hXXp://blog.northpointindia.com/gKBwOvxeq
Further Reading:
rebus snippets
Tuesday, May 12, 2015
Indicators - Geodo Malware Part 2
I have some more Geodo/Feodo indicators for you since yesterdays posting. If this keeps up I will make a page dedicated to Geodo indicators similar to the one I created for the Houdini RAT.
Threat Name: Geodo
File Download Locations:
These are live malware files, download with caution.
hXXp://altvramagazine.com:80/wp-content/themes/altura/cr_mss3.exe
hXXp://www.hairlosstreatments4u.com:80/4KVHAGFUPB/949.exe
hXXp://arasshahintools.com:80/wp-content/themes/darya/cr_mss3.exe
hXXp://www.greago.com:80/wp-content/themes/flowmaster/cr_mss3.exe
hXXp://holyspirit.wa.edu.au:80/wp-content/uploads/cr_mss3.exe
hXXp://heliosradio.com:80/WGNz20QXeyK/9049.exe
hXXp://photowaaley.com:80/2g9IiGaouYBOQ/9049.exe
hXXp://region-magdeburg.ramminger-berlin.de:80/modules/mod_aratipas/cr_mss3.exe
hXXp://jomigym.nl:80/80dUCBiJXg/9049.exe
hXXp://tasheelseries.com.au:80/modules/mod_aratipas/cr_mss3.exe
Virustotal File Analysis:
9049.exe
Command and Control Servers:
Request Method: POST
94.126.171.85:8080
94.176.2.168:8080
103.16.26.36:8080
37.59.0.141:8080
46.32.233.226:8080
76.74.252.88:8080
99.249.191.195:8080
Enjoy! Look out for a new indicator list for this malware.
Threat Name: Geodo
File Download Locations:
These are live malware files, download with caution.
hXXp://altvramagazine.com:80/wp-content/themes/altura/cr_mss3.exe
hXXp://www.hairlosstreatments4u.com:80/4KVHAGFUPB/949.exe
hXXp://arasshahintools.com:80/wp-content/themes/darya/cr_mss3.exe
hXXp://www.greago.com:80/wp-content/themes/flowmaster/cr_mss3.exe
hXXp://holyspirit.wa.edu.au:80/wp-content/uploads/cr_mss3.exe
hXXp://heliosradio.com:80/WGNz20QXeyK/9049.exe
hXXp://photowaaley.com:80/2g9IiGaouYBOQ/9049.exe
hXXp://region-magdeburg.ramminger-berlin.de:80/modules/mod_aratipas/cr_mss3.exe
hXXp://jomigym.nl:80/80dUCBiJXg/9049.exe
hXXp://tasheelseries.com.au:80/modules/mod_aratipas/cr_mss3.exe
Virustotal File Analysis:
9049.exe
Command and Control Servers:
Request Method: POST
94.126.171.85:8080
94.176.2.168:8080
103.16.26.36:8080
37.59.0.141:8080
46.32.233.226:8080
76.74.252.88:8080
99.249.191.195:8080
Enjoy! Look out for a new indicator list for this malware.
Monday, May 11, 2015
Indicators - Geodo Malware
I have been seeing an influx of Geodo malware and have compiled some data on finding this infection on your network.
Threat Name: Geodo
File Download Locations:
These are live malware files, download with caution.
Threat Name: Geodo
File Download Locations:
These are live malware files, download with caution.
| hXXp://altvramagazine.com:80/wp-content/themes/altura/cr_mss3.exe |
| hXXp://aqua-system.com.ua/AXMqjiFob |
| hXXp://arasshahintools.com:80/wp-content/themes/darya/cr_mss3.exe |
| hXXp://bicycle.ns.ca:80/wp-content/themes/shadow/cr_mss3.exe |
| hXXp://conservation-wildlife.asn.au/eSxai7o0d/Status_zu_Sendung_916907832086.zip |
| hXXp://cucifineart.com/wp-content/Z5LIHdweGyb/Status_zu_Sendung_916907832086.zip |
| hXXp://dpsharma.com/wp-content/themes/twentyfifteen/Hvcmrq2un/Status_zu_Sendung_916907832086.zip |
| hXXp://fcmtravel.co.ke/7HTCkvNV |
| hXXp://www.allcameras.tk:80/wp-content/themes/twentyfifteen/cr_mss3.exe |
| hXXp://www.hairlosstreatments4u.com:80/4KVHAGFUPB/949.exe |
| hXXp://www.hertzlease.com.mt:80/mCVXg3ucvfG/949.exe |
Virustotal File Analysis:
Command and Control Servers:
Request Method: POST
121.50.46.81:8080
173.230.130.252:8080
188.165.235.13:8080
192.126.123.10:8080
192.163.204.172:8080
200.159.128.189:8080
200.75.7.92:8080
201.175.17.35:8080
42.62.40.103:8080
User-agent Strings:
I have yet to determine if these are unique to the malware or not, so please be careful using them to block and/or detect malicious network traffic. If anyone has anymore information on these, then please leave a comment.
Mozilla/5.0 (compatible; MSIE 9.0; Windows NT 7.1; Trident/5.0)
Mozilla/5.0 (Windows; U; MSIE 7.0; Windows NT 6.0; en-US)
Further Reading:
Geodo Tracker - website dedicated to tracking all Geodo information. The owner of the site has a blog as well and is well worth the reading.
Hybrid Analysis Results - sandbox analysis results for the executable of the zip file listed above.
Thursday, April 16, 2015
Houdini / h-worm / njRAT Tracking List
I added a tracking list for the Houdini malware (njRAT, h-worm, etc...). This list is best used in a monitoring tool rather than a blocking tool as some of the domains will most likely be out-of-date. If you are not familiar with this malware, then please check out the links listed below.
This list has grown over the past year since I have been tracking it, so I hope it serves you well. I will continue to update the list as I find new variants or indicators, and if you wish to contribute then please feel free to send me an email.
Click here to go to the page. Enjoy!
Further reading:
This list has grown over the past year since I have been tracking it, so I hope it serves you well. I will continue to update the list as I find new variants or indicators, and if you wish to contribute then please feel free to send me an email.
Click here to go to the page. Enjoy!
Further reading:
Tuesday, April 14, 2015
Incoming Houdini Tracking List
I have been seeing a good amount of Houdini traffic in the past, and it seems to be picking up steam again: for a quick refreshed, check out this FireEye report. So I decided to create a list of command and control servers used by the malware.
The list will not be an active/live list such as the ones you find on Abuse.ch, rather it will contain historical data of hosts, as well as other useful information such as user-agent string values, HTTP URI paths, destination ports, and other data.
The list should be posted within the week, so please check back.
The list will not be an active/live list such as the ones you find on Abuse.ch, rather it will contain historical data of hosts, as well as other useful information such as user-agent string values, HTTP URI paths, destination ports, and other data.
The list should be posted within the week, so please check back.
Friday, March 20, 2015
Indicators - Zbot Variant
Apologies for not updating for a while, but I think this post willThis one has been showing up pretty frequently. I have labeled it as Zbot, but it is most likely Dridex or Upatre; if anyone has clarification then please let me know.
Threat Name: Zbot / Upatre / Dridex
Indicators: The malware will attempt a connection to the "checkip.dyndns.org" domain in order to ensure connectivity. If successful, then it will attempt to connect to several IP addresses (direct to IP over HTTP) using high level ports. It's hard to nail down exact domain names and IP addresses, but thankfully there are other indicators.
HTTP Indicators:
Threat Name: Zbot / Upatre / Dridex
Indicators: The malware will attempt a connection to the "checkip.dyndns.org" domain in order to ensure connectivity. If successful, then it will attempt to connect to several IP addresses (direct to IP over HTTP) using high level ports. It's hard to nail down exact domain names and IP addresses, but thankfully there are other indicators.
HTTP Indicators:
- Request Methods
- CONNECT - this method will be used to connect to "checkip.dyndns.org" to determine network connectivity.
- POST - will connect to a domain with a URI path of "/gate.php".
- GET
- User-agent Strings:
- Mazilla/4.0
- Mazilla/5.0
- HTTP URI Paths:
- /gate.php
- /1802us21/
- /1902us21/
- /2101us21/
- /2901us21/
- /mandoc/
- /images/
- /news/
- /files/
- /fla/
- /ar/file/
- /menu/
- /dhl/
- HTTP URI Filenames:
- /factj.pdf
- /gunter.pdf
- /hone.pdf
- /sdocc.pdf
Subscribe to:
Posts (Atom)